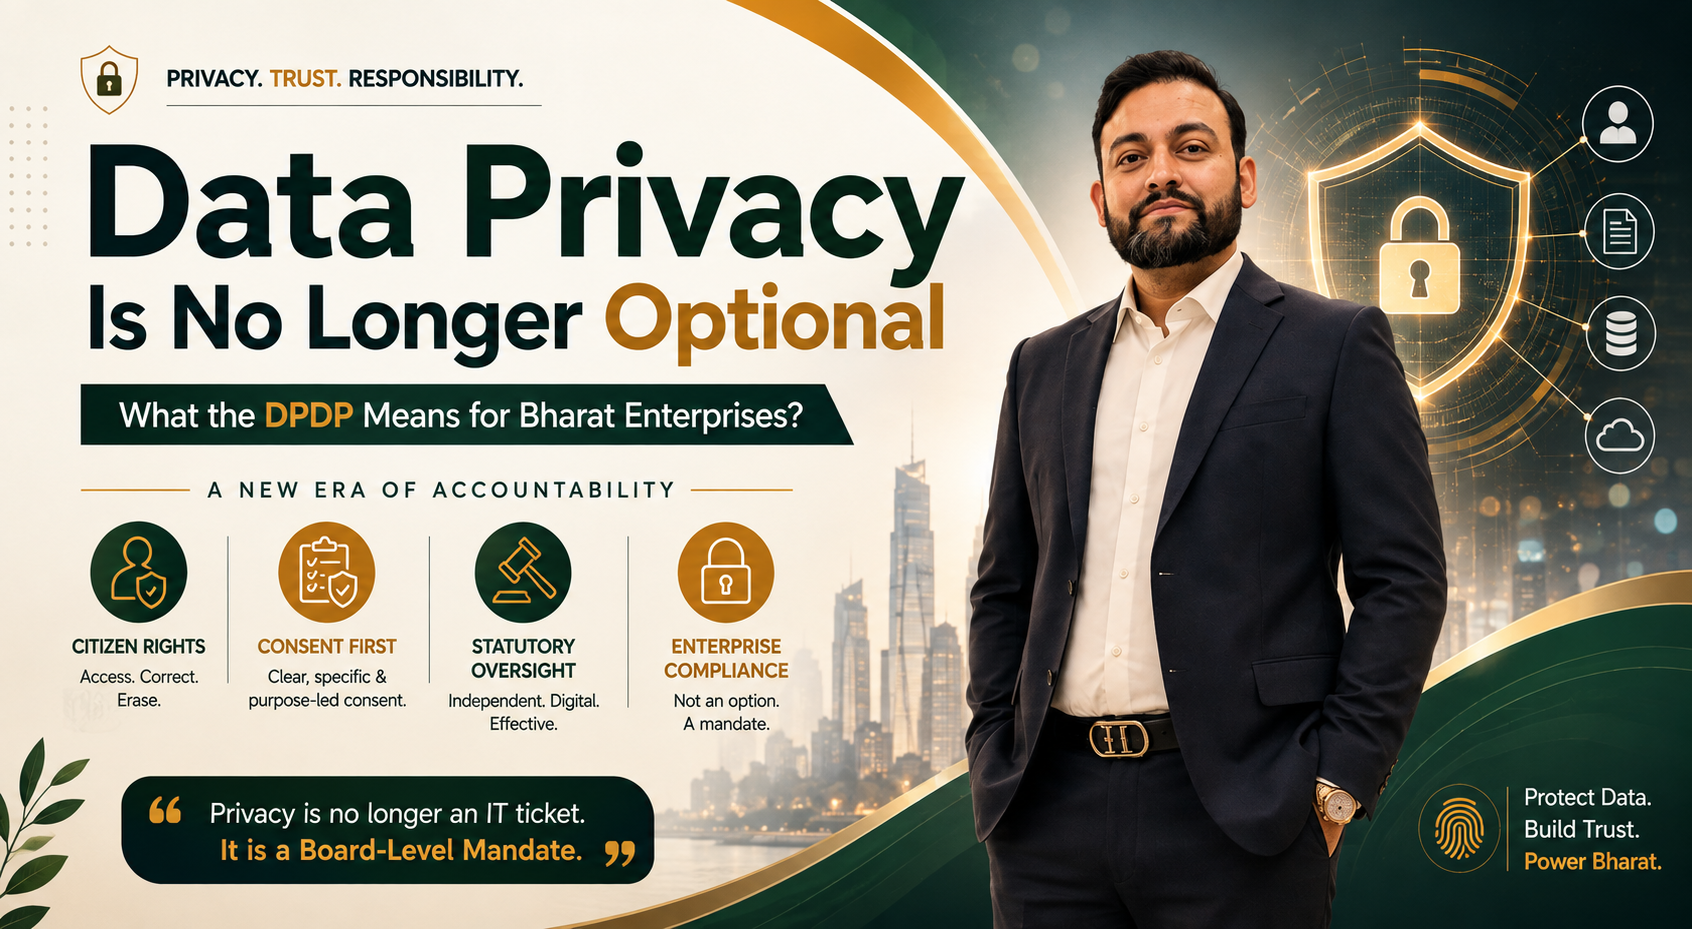
Data Privacy Is No Longer Optional
What the DPDP Means for Bharat Enterprises?
By Shri Nitin Tiwari, Chairman, Aarav Global Group

Be candid with me, for years, consumer data across Bharat was treated like oxygen in the room as freely gathered, and largely unmeasured; whether a user typed a query into a search bar or entered basic details into an app, their information quietly landed in third-party data pits, explicitly oversighted, am I right?
From where I sit in the boardroom, I can tell you that this era of informal data collection is officially behind us. With the arrival of the Digital Personal Data Protection (DPDP) framework and its underlying rules, privacy is no longer an IT support ticket, it is now a board-level operational mandate across Bharat.
The Big Reset: Why the DPDP Framework Exists
Legacy laws relied on vague guidelines designed for an earlier internet era. The DPDP framework introduces three massive changes:
- Clear Rights for Citizens: Citizens (Data Principals) hold statutory rights to access, correct, or completely erase their personal information.
- Consent-First Architecture: Pre-ticked consent boxes and generic terms of service are invalid. Data collection requires clear, affirmative, purpose-led notices.
- Direct Statutory Oversight: The Data Protection Board of Bharat operates as an independent, fully digital regulatory body designed to audit breaches, handle grievances, and enforce compliance.
What Changes for Enterprises in Bharat?
Under the Act, any business that determines why and how personal data gets processed is classified as a Data Fiduciary. That classification covers almost every consumer-facing enterprise, HR department, and tech vendor operating within Bharat.
The Operational Shift
- Itemized, Multilingual Notices: Privacy notices must explicitly outline what data is collected and for what precise purpose. They must be accessible in English and all 22 languages specified in the Eighth Schedule to the Constitution of Bharat.
- Child Data Controls: Processing data for users under 18 requires verifiable parental consent, with strict bans on tracking, profiling, or targeted ads directed at minors.
- Significant Data Fiduciaries (SDFs): High-risk or high-volume data handlers face mandatory requirements, including Data Protection Impact Assessments (DPIAs), independent data audits, and appointing a resident Data Protection Officer (DPO).
The Regulatory Interplay: RBI Rules & IndiaAI
The DPDP framework interacts directly with sector regulators and national technology initiatives.
Financial Entities and the RBI Dual-Layer
For banks, NBFCs, and fintechs, compliance requires balancing Reserve Bank of Bharat (RBI) regulations with DPDP mandates:
- Retention vs. Erasure: The RBI mandates storing transaction and KYC logs for extended periods (typically 7 to 10 years), while the DPDP Act requires erasing personal data once its original purpose ends. Financial platforms must deploy automated data-tagging systems to preserve regulatory audit records under RBI rules while purging non-essential marketing data.
- Unbundled Financial Consent: Aligning with RBI digital lending directives, DPDP rules forbid bundling consent. Obtaining permission to process a credit check cannot double as consent for cross-selling insurance or tracking alternative device data.
The IndiaAI Vision and Responsible Deployments
As enterprises across Bharat scale artificial intelligence through the IndiaAI Mission, privacy laws dictate how algorithms operate:
- Consented Training Sets: Customer data scraped without explicit consent cannot feed enterprise AI models.
- Algorithmic Transparency: High-risk automated decisioning (such as credit scoring or underwriting) requires clean data lineage, driving enterprises toward privacy-enhancing technologies like federated learning.
The Phased Implementation Timeline
My role is to ensure both my organisation and my leadership team are fully aligned with the structured transition phases ahead:
Phase 1: Institutional Infrastructure
Establishing the baseline regulatory framework through the formal notification of DPDP Rules and setting up the Data Protection Board to oversee enforcement.
Phase 2: Consent Manager Ecosystem
Deploying interoperable Consent Manager platforms that empower citizens to seamlessly grant, review, or revoke data access permissions across digital services.
Phase 3: Substantive Compliance
Reaching full operational enforcement, requiring complete execution of itemized notices, verifiable parental consent workflows, and strict 72-hour breach reporting protocols.
What Non-Compliance Means for Enterprises in Bharat
While the Act avoids criminal imprisonment, treating data carelessly introduces severe operational, legal, and commercial exposure:
- Statutory Regulatory Directives: The Data Protection Board holds authority to demand processing logs, conduct investigations, and issue binding directives to freeze non-compliant data pipelines.
- Mandatory Breach Disclosures: Concealing or delaying personal data breach reports is explicitly illegal. Organizations must notify both the regulator and affected users within 72 hours.
- Supply Chain Disqualification: Enterprise software buyers, global partners, and corporate clients now require verified DPDP compliance before executing vendor contracts.
- Consent Revocation Risk: Once Consent Managers go live, customers can withdraw access permissions with a single click, instantly halting data streams for non-compliant brands.
Priority Action Items for Business Leaders
Enterprises should prioritize four foundational steps:
- Map Your Data Lineage: Audit all internal and vendor pipelines to track where personal data originates, where it resides, who processes it, and when it gets deleted.
- Update Vendor Contracts: Re-architect agreements with third-party data processors to enforce strict security standards and rapid 72-hour breach notification windows.
- Redesign Onboarding Interfaces: Replace legacy "Accept Terms" buttons with explicit, itemized, and multilingual opt-in consent prompts.
- Build Incident Response Protocols: Prepare automated internal procedures to detect, contain, and report security incidents without delay.
My Concluding Remarks
It is easy to look at a new framework and see friction, but as leaders, we must see the trail it clears for us. Let us view this transition not as a hurdle to jump, but as a green light that accelerates digital adoption, levels the playing field, and elevates Bharat's enterprise ecosystem onto the global stage.
At Aarav Global Group, we are on the verge of launching an innovative AI-powered platform that empowers organizations to attain, measure, and continuously maintain compliance with the Digital Personal Data Protection (DPDP) Act through a streamlined, intelligent, and efficient approach!
Comments
No comments yet. Be the first!
Leave a Comment